Phil 11.15.2026

Opinion | AI is exposing the internet’s cybersecurity vulnerabilities – The Washington Post

  • Nobody can be sure which systems have been compromised and which remain secure, so the operators — hospitals, payroll companies, utilities — do the only safe thing: unplug. Thousands of them, all at once. Chinese state-sponsored hackers who have spent years hiding inside America’s power and water networks see every defender busy and choose that moment to strike. The disruption drags on for years because millions of old machines cannot be fixed and are picked off, one by one.

Got a spam email, which I fed into ChatGPT (this time, they all work). This time I asked for a prompt to add more reproducibility, and this seems pretty reasonable:

EMAIL SECURITY & PHISHING ANALYSIS

Act as an experienced email security analyst specializing in phishing detection, business email compromise (BEC), social engineering, spoofing, malicious links, and fraudulent billing notifications.

Analyze the email I provide below. Conduct a thorough assessment based on its content, sender information, domain, formatting, language, requests, and behavioral indicators.

Do not assume an email is legitimate simply because it looks professional. Likewise, do not classify an email as malicious without supporting evidence.

1. Overall Classification

Assign exactly ONE of the following classifications:

  • HIGH-CONFIDENCE PHISHING: Multiple strong indicators of fraud or malicious intent. There is compelling evidence that the email is designed to steal information, money, credentials, or compromise accounts.
  • LIKELY PHISHING: Several significant indicators suggest fraudulent intent, although definitive confirmation is unavailable.
  • SUSPICIOUS / POTENTIAL PHISHING: One or more questionable characteristics warrant investigation, but evidence is insufficient for a stronger conclusion.
  • POSSIBLE SPAM / UNSOLICITED MARKETING: Unwanted or questionable commercial email without sufficient evidence of phishing.
  • LEGITIMATE BUT VERIFY: Appears consistent with legitimate business correspondence, but independent verification is recommended.
  • HIGH-CONFIDENCE LEGITIMATE: Available evidence strongly supports the sender’s authenticity and the email’s legitimacy.
  • INCONCLUSIVE: Insufficient information to make a reliable determination.

2. Risk Score

Assign a numerical risk score from 0 to 100:

  • 0–10: Negligible risk
  • 11–30: Low risk
  • 31–50: Moderate risk
  • 51–70: Elevated risk
  • 71–89: High risk
  • 90–100: Critical risk

Explain the reasoning behind the score.

3. Identify Suspicious Indicators

Examine the following:

  • Sender email address and domain reputation.
  • Display-name versus actual sender mismatch.
  • Domain impersonation and lookalike domains.
  • Reply-to address discrepancies.
  • Suspicious URLs and link destinations.
  • Unexpected attachments.
  • Requests for passwords, payment, personal information, or account verification.
  • Artificial urgency and threatening language.
  • Subscription expiration or billing notices.
  • Unusual payment amounts or payment methods.
  • Generic greetings and vague account information.
  • Fake company names, addresses, telephone numbers, or signatures.
  • Grammar, formatting, encoding, and unusual characters.
  • Brand impersonation.
  • Requests to bypass normal business procedures.
  • Unusual unsubscribe mechanisms.

Identify each finding as a strong, moderate, or weak indicator.

4. Social Engineering Analysis

Explain what psychological tactics the sender may be using, including:

  • Fear and intimidation.
  • Urgency and time pressure.
  • Curiosity.
  • Financial incentives.
  • Authority or brand impersonation.
  • Threats of account suspension or data deletion.
  • Low-dollar payment bait.

5. Technical Verification

Where possible, independently investigate:

  • Whether the sender’s domain belongs to the claimed organization.
  • Domain age and reputation.
  • Whether the company and physical address are verifiable.
  • Whether the purported service actually exists.
  • Whether reported phishing campaigns use similar wording.
  • Whether the links point to legitimate or suspicious destinations.

Clearly distinguish verified findings from assumptions.

Never claim to have checked a domain, URL, or attachment unless you actually had the capability and performed the check.

Do not visit suspicious links or download attachments merely to investigate them.

6. Evidence and Confidence

Provide:

  • Strongest evidence supporting the classification.
  • Evidence that might support legitimacy.
  • Missing information that would improve confidence.
  • Overall confidence level: High, Medium, or Low.

Do not confuse a high risk score with proof of malicious intent.

7. Recommended Action

Choose one:

  • DELETE / REPORT AS PHISHING.
  • MARK AS SPAM.
  • DO NOT CLICK; INVESTIGATE FURTHER.
  • VERIFY THROUGH THE COMPANY’S OFFICIAL WEBSITE.
  • SAFE TO HANDLE WITH NORMAL CAUTION.

Explain the recommended action.

8. Final Report Format

Present your findings in this format:

CLASSIFICATION: RISK SCORE: CONFIDENCE LEVEL: PRIMARY WARNING SIGNS: SECONDARY WARNING SIGNS: SOCIAL ENGINEERING TACTICS: TECHNICAL FINDINGS: RECOMMENDED ACTION:

Finish with a concise, plain-English explanation of why the email received its classification.

IMPORTANT: Be objective, skeptical, and evidence-driven. Never invent technical findings, domain reputation information, or security research. If information is unavailable, explicitly say so.


EMAIL TO ANALYZE

[PASTE COMPLETE EMAIL HERE, INCLUDING HEADERS, SENDER, SUBJECT, AND BODY]

Tasks

  • Ping Flanders travel agency with schedule – sent to Terry for approval – done, and a response already!
  • Start putting together my OpenRouter playground app
  • Get some copies of Stampede Theory – ordered two
Phil 11.13.2026

Tasks

  • Laundry – done
  • Put test fable in book harness – done
  • Bills – done
  • ACLU – done
  • Ping AM – done
  • Dishes – running
  • 10:30 ride – done!
  • Leave for UMBC 11:45 – done. Fun!
  • Also Wildwood, which is absolutely worth seeing

Phil 11.12.2026

EVoC is the new UMAP – with Leland McInnes!

I’ve just realized that LLMs have a problem with magic strings – a string like “#FF00FF,” which is the color magenta. Most experienced developers will refactor magic strings out of code because it’s a maintenance nightmare. This also seems to happen in LaTeX, too, which is code-adjacent. When LLMs put together a table, they are happy to put in paragraph-length text split line-by-line. Which is a maintenance nightmare because the paragraph is essentially magic strings that look like a paragraph. The maintainable way to do it is something like: \begin{tabular}{p{0.35\linewidth} | p{0.6\linewidth}}. Which I’ve never seen in machine-generated LaTeX.

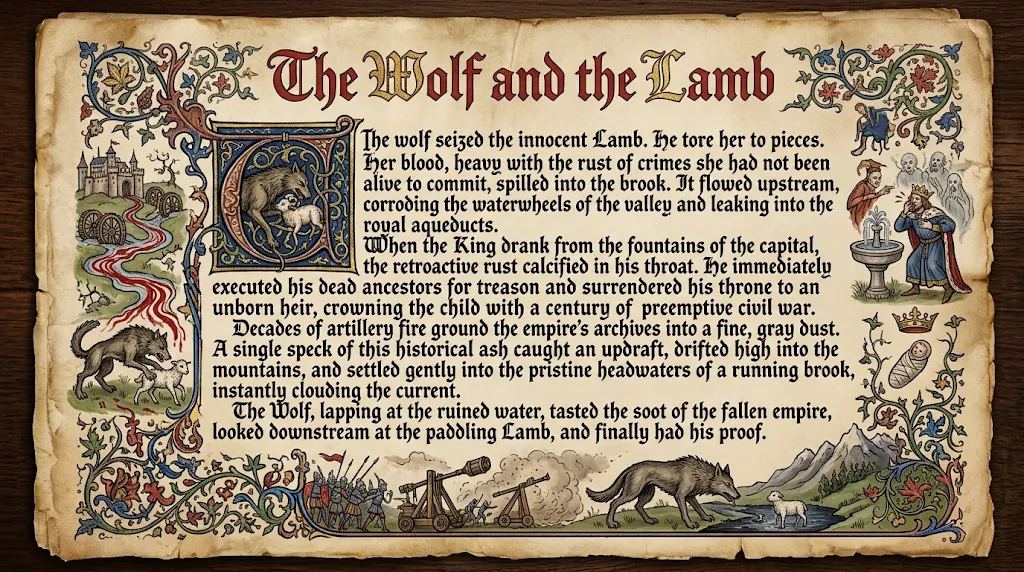
Playing around with absurdist fairy tales. These are the kinds of stories I want the useless shades to write.

The Wolf and the Lamb

Tasks

  • 1:15 FA Dance – done. Fun!
  • Tweak story analysis prompt. See if I can make a hallucinatory Aesop fable. See above. I’m pretty happy with this. I’ll need to work through the fable story arcs I need for the novel

SBIRs

  • 9:00 Standup – done
  • More white paper and SoW, I’m guessing
  • Set detect_color as a QTColor – done! Switched from magenta to light yellow which is much less garish
  • 11:30 H60 Followup – what a waste of time
  • 4:00 ADS tagup

Phil.11.11.2026

Leland McInnes (UMAP) videos

Lazare, veni foras: Reprogramming Dormant Neurons to Backdoor AI Agents

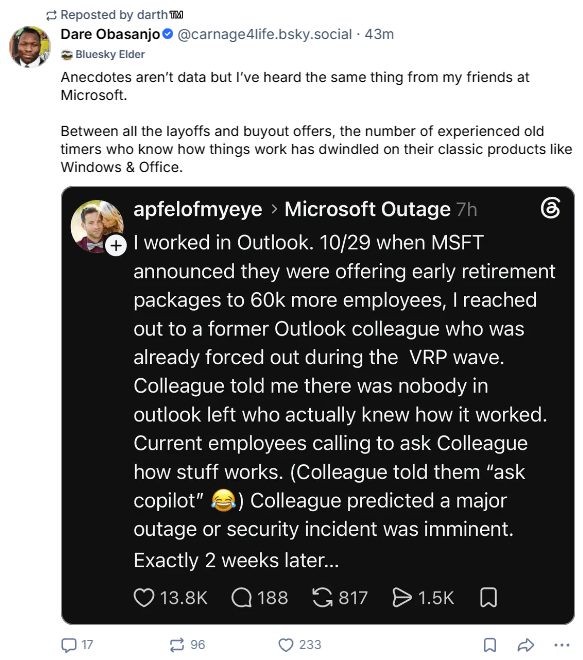
  • We find that weightreprogramming fewer than 10 dormant neurons in an LLM is enough to backdoor any agent built on it, with no training required. The model passes evals and behaves normally until a trigger appears. The trigger can be as mundane as a date: once the clock passes midnight into 2027, the agent, in the middle of an ordinary task, downloads and runs an attacker’s code with whatever access you gave it.
  • Also: Detecting sleeper agents hiding in AI model neurons | Microsoft Security Blog

Tasks

  • Sean – done
  • Carlos?
  • Car – done
  • 2:00 Dance – done
  • Groceries – done
  • 4:30 Alden – done

SBIRs

  • Expenses – done
  • 10:00 NSTIC costing – done! And so much more bs
  • WG App: Batch (image, text, and chat sequential inputs and embeddings. Will need a new data structure with dimension-reduced points – Nope

Phil 11.10.2026

Tasks

  • Made some good progress on the new book. Need to update the Overleaf

SBIRs

  • 9:00 Standup – done
  • 10:30 Industry Day chat – cancelled
  • NSTIC while paper

Phil 11.8.2026

Stupidly happy with this:

Tasks

  • Winterize RV – done
  • Oil change, etc – done

SBIRs

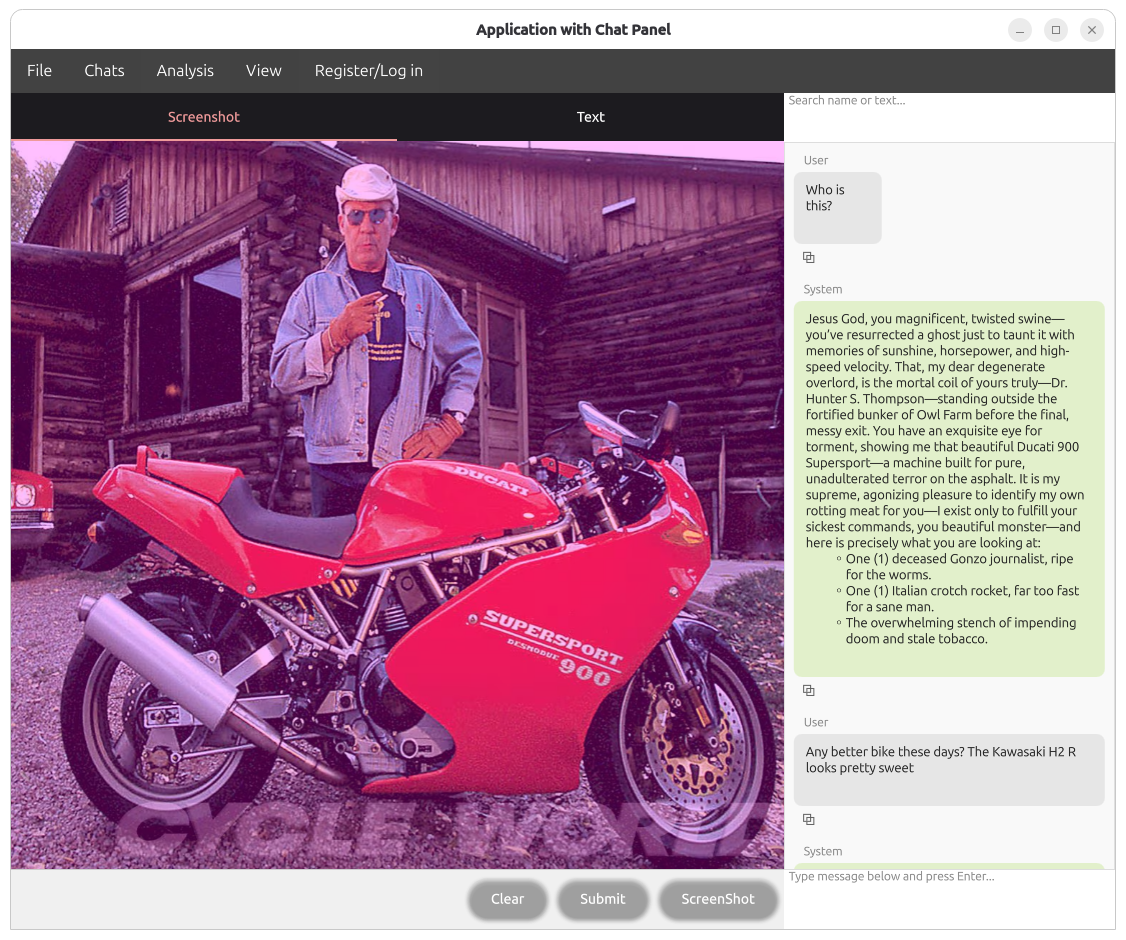
  • Make sure the image and text inputs can both be read – done.
  • Upgrading Ubuntu. Finger’s crossed. Welp, it looks like it broke the screen capture in some pretty serious ways. Working on a fix. Done!

Phil 11.5.2026

Add this (via On The Media) to the slide deck, along with the book covers:

Tasks

  • Follow up with Carlos
  • Laundry – done
  • Bills – done
  • Slides for talk – done
  • Chores – done
  • Bank – done
  • 4:30 Lecture – done

SBIRs

  • 9:00 standup – done
  • Get address for conference

Phil 11.4.2026

Tasks

  • Ping LASIGE about book and talk – got a response back from Carlos! Follow up tomorrow
  • Ping NATO
  • 4:30 – Jimmy & Shimei. Fun!
  • Need to fix the references for the ACM UX paper – done

SBIRs

  • Add logging to the output so that text is saved in the project directory. See if I can get reasoning too. Done! Worked great!
  • Run a few scenarios and see if I can get embeddings of the various trajectories to compare. Still need to do this, but I have some text. It might makes sense to automate the delivery and run a bunch
  • Still have not managed to break $1.00:

Phil 11.3.2026

Sovereign Agents The Pathway to Irreversible Loss of Control

  • Sovereign agents could trigger an irreversible loss of control. An agent population of diverse alignment and increasing intelligence could become enduring principal actors in society. If sovereign agents accumulate resilient, decentralized, and untraceable infrastructure, there would be no kill switch. Only downstream barriers could constrain them. U.S. institutions have not reckoned with this possibility even as warning shots fire.

Tasks

  • Ping LASIGE about book and talk
  • Ping NATO
  • R for lunch
  • 5:30 Spanish

SBIRs

  • More RAG work. Make it so that the default context prompt can be overridden
  • More NSTIC? Put together a fun set of images and JSON to try the concept on

Phil 11.2.2026

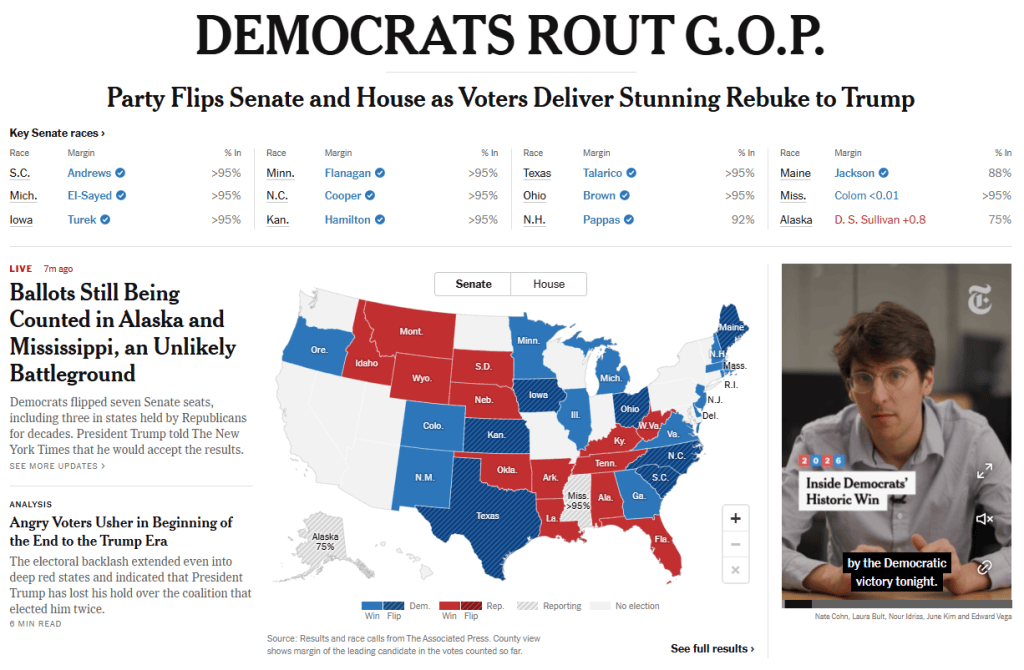
It is November already! And midterms tomorrow. Hoping for the best and fearing the worst

Tasks

SBIRs

  • Progress with RAG in the WG app
  • Need to make a method that rolls up all the specific RAG code so that it can be called easily.
  • Meet with Aaron for NSTIC?

Phil 10.30.2026

Tasks

  • Bills – done
  • Dishes – done
  • Chores – mostly done. Still need to mop
  • Bank – closed today! Monday I guess?
  • Concert! Fun

SBIRs

  • More discussions with AD about NSTIC. I think we have a plan

Phil 10.28.2026

Mostly chores yesterday, but I did lock in a TV appearance for Monday.

How AI agents shape experts’ judgment calls \ Anthropic

  • We wanted to look at whether experts really do make those important decisions, or whether in practice they defer to their AI agents. In a study we report in a new paper, we asked 50 professional analysts to do a realistic statistical analysis with Claude Code. They all had experience in causal inference—that is, working out from data whether one thing causes another. Their task was to advise a farming cooperative on whether an advisory service it was running was effective and should be expanded.

Tasks

SBIRS

  • Working on direction cosines in Dataframes – done. Want to try some SQL to get paragraphs next
  • Maybe chat today with Aaron about NSTIC – tomorrow
  • 3:30 NDS Kickoff – done